Nginx Reverse Proxy Setup with SSL: Complete Guide 2026

Setting up a reverse proxy is essential for modern web applications. This nginx reverse proxy setup guide covers everything you need to know in 2026, from basic configuration to SSL encryption with Let’s Encrypt. Whether you’re managing a single application or multiple microservices, Nginx remains the gold standard for reverse proxy solutions.
What Is a Reverse Proxy and Why Use Nginx?
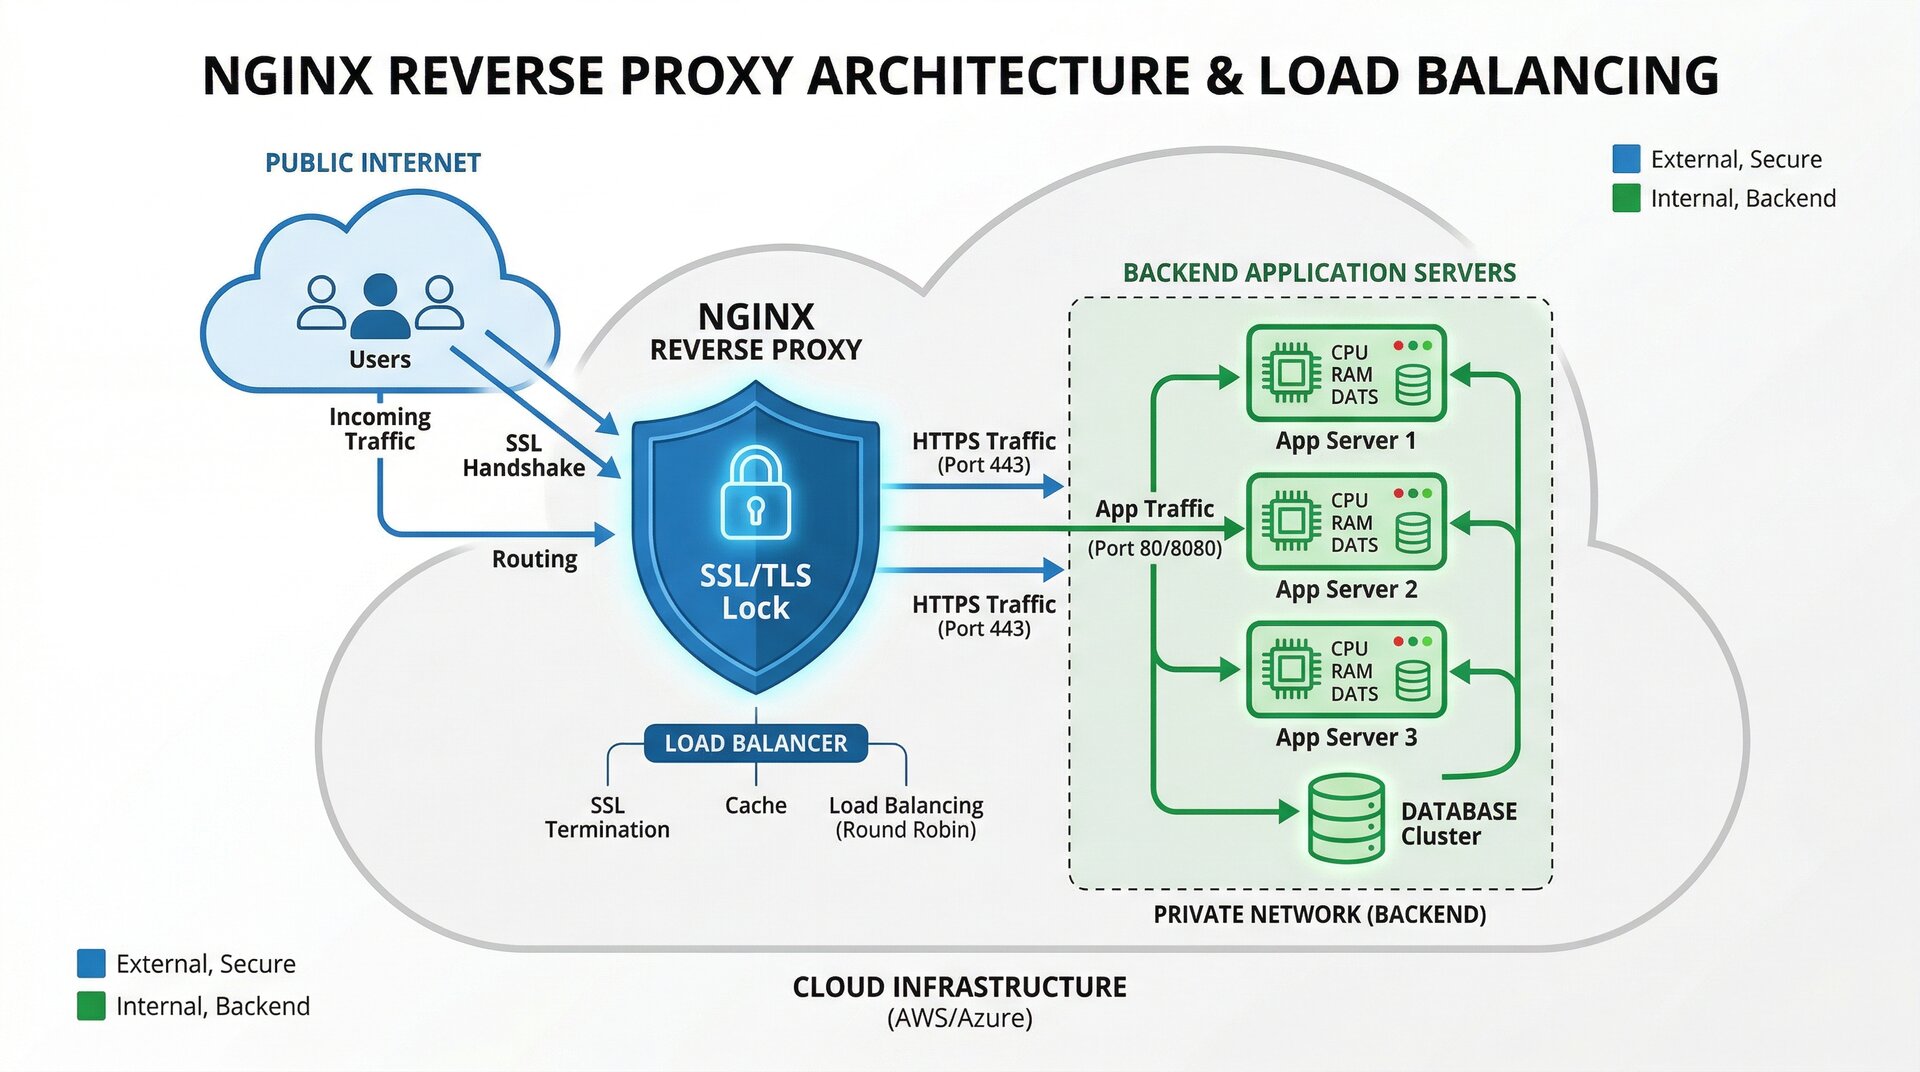
A reverse proxy acts as an intermediary between client requests and backend servers. When you implement an nginx reverse proxy setup, you gain several advantages: improved security through IP masking, load balancing capabilities, SSL termination, and simplified domain management. Nginx handles thousands of concurrent connections with minimal resource usage, making it ideal for production environments.
The nginx reverse proxy setup process has evolved significantly. Modern configurations prioritize security headers, HTTP/2 support, and automated certificate management. Understanding these fundamentals ensures your web infrastructure remains robust and scalable.
Prerequisites for Your Nginx Reverse Proxy Setup
Before beginning the nginx reverse proxy setup, ensure you have:
- A Linux server (Ubuntu 22.04/24.04 or Debian 12 recommended)
- Root or sudo access
- A domain name pointing to your server
- Backend application running on a local port
For this tutorial, we’ll assume your backend application runs on port 3000. The nginx reverse proxy setup can accommodate any port or multiple backend services.
Step 1: Installing Nginx
Start your nginx reverse proxy setup by installing the web server. Open your terminal and execute:
sudo apt update
sudo apt install nginx -y
Enable and start the Nginx service:
sudo systemctl enable nginx
sudo systemctl start nginx
Verify installation by accessing your server’s IP address in a browser. You should see the Nginx welcome page, confirming the foundation of your nginx reverse proxy setup is ready.
Step 2: Configuring the Reverse Proxy
The core of any nginx reverse proxy setup lies in the server block configuration. Create a new configuration file:
sudo nano /etc/nginx/sites-available/myapp
Add the following configuration for your nginx reverse proxy setup:
server {
    listen 80;
    server_name example.com www.example.com;

    location / {
        proxy_pass http://localhost:3000;
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
These headers ensure your backend application receives accurate client information. The nginx reverse proxy setup passes the original host, IP address, and protocol scheme.
Enable the configuration by creating a symbolic link:
sudo ln -s /etc/nginx/sites-available/myapp /etc/nginx/sites-enabled/
Test your nginx reverse proxy setup configuration:
sudo nginx -t
If successful, reload Nginx:
sudo systemctl reload nginx
Step 3: Securing with SSL Certificates
No nginx reverse proxy setup is complete without SSL encryption. Let’s Encrypt provides free certificates through Certbot. Install the necessary packages:
sudo apt install certbot python3-certbot-nginx -y
Obtain and automatically configure SSL certificates:
sudo certbot --nginx -d example.com -d www.example.com
Certbot modifies your nginx reverse proxy setup to include HTTPS redirection and SSL configuration. The process creates automatic renewal cron jobs, ensuring your certificates never expire.
Advanced Nginx Reverse Proxy Setup Options
WebSocket Support
Modern applications require WebSocket connections. Extend your nginx reverse proxy setup with these directives:
location /ws {
    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection "upgrade";
    proxy_pass http://localhost:3000;
}
Load Balancing Multiple Backends
For high-traffic applications, distribute requests across multiple servers:
upstream backend {
    server 192.168.1.10:3000;
    server 192.168.1.11:3000;
}

server {
    location / {
        proxy_pass http://backend;
    }
}
Rate Limiting
Protect your applications from abuse by adding rate limiting to your nginx reverse proxy setup:
limit_req_zone $binary_remote_addr zone=mylimit:10m rate=10r/s;

server {
    location / {
        limit_req zone=mylimit burst=20 nodelay;
        proxy_pass http://localhost:3000;
    }
}
Security Hardening for 2026
Enhance your nginx reverse proxy setup with these security headers:
add_header X-Frame-Options "SAMEORIGIN" always;
add_header X-Content-Type-Options "nosniff" always;
add_header X-XSS-Protection "1; mode=block" always;
add_header Referrer-Policy "strict-origin-when-cross-origin" always;
Disable server tokens to hide your Nginx version:
http {
    server_tokens off;
}
Troubleshooting Common Issues
When your nginx reverse proxy setup encounters problems, check these common solutions:
- 502 Bad Gateway: Verify your backend application is running and accessible on the specified port
- SSL certificate errors: Ensure your domain DNS points correctly to the server IP
- Permission denied: Check that Nginx has proper read permissions for static files
- Configuration errors: Always test with
1nginx -t
before reloading
Review Nginx error logs for detailed diagnostics:
sudo tail -f /var/log/nginx/error.log
Performance Optimization Tips
Maximize your nginx reverse proxy setup efficiency with these optimizations:
proxy_cache_path /var/cache/nginx levels=1:2 keys_zone=my_cache:10m max_size=1g;

server {
    location / {
        proxy_cache my_cache;
        proxy_cache_valid 200 301 302 10m;
        proxy_pass http://localhost:3000;
    }
}
Enable gzip compression for faster content delivery:
gzip on;
gzip_types text/plain text/css application/json application/javascript;
Related Architecture Guides: Running backends in containers? Read our guide on deploying containerized web applications with Docker and strengthen the underlying host with our infrastructure security hardening recommendations.
Conclusion
This nginx reverse proxy setup guide provides a solid foundation for securing and scaling your web applications. From basic configuration to advanced load balancing and caching, Nginx offers the flexibility needed for modern infrastructure. Remember to regularly update your server and monitor logs for optimal performance. Start implementing your nginx reverse proxy setup today and experience improved security, performance, and manageability.
- About the Author
- Latest Posts

Mark is a senior content editor at Text-Center.com and has more than 20 years of experience with linux and windows operating systems. He also writes for Biteno.com