How to Secure Ubuntu Server 2026: Complete SSH Hardening and Firewall Setup Guide

Why Ubuntu Server Security Matters in 2026
In 2026, ubuntu server security 2026 is more critical than ever. With cyber threats evolving rapidly, hardening your Ubuntu server isn’t optional—it’s mandatory. According to recent security reports, improperly configured SSH and firewall settings remain the top attack vectors for server breaches.
This comprehensive guide walks you through the essential steps to secure Ubuntu Server 2026, from SSH hardening to firewall configuration. Whether you’re deploying a new server or auditing an existing one, these best practices will protect your infrastructure against modern threats.
Understanding Ubuntu Server Security 2026 Fundamentals
Before diving into configurations, let’s establish the security foundation. Ubuntu Server security in 2026 revolves around three core principles:
- Principle of Least Privilege: Grant only the minimum permissions necessary for users and services
- Defense in Depth: Layer multiple security controls so if one fails, others still protect
- Security by Default: Disable unnecessary services and lock down configurations from the start
These principles guide every recommendation in this tutorial. Let’s start with the most critical component: SSH hardening.
Step 1: Harden SSH Configuration
SSH is your primary remote access method, making it a prime target. Here’s how to lock it down for ubuntu server security 2026 compliance:
Disable Password Authentication
Password-based SSH is vulnerable to brute-force attacks. Switch to SSH key authentication immediately:
2
3
4
5
6
7
8
ssh-keygen -t ed25519 -C "[email protected]"
# Copy public key to Ubuntu server
ssh-copy-id -i ~/.ssh/id_ed25519.pub username@your_server_ip
# Test SSH key login before disabling passwords
ssh -i ~/.ssh/id_ed25519 username@your_server_ip
Once SSH key authentication works, edit the SSH daemon configuration:
Make these critical changes for ubuntu server security 2026:
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
PasswordAuthentication no
# Disable root login via SSH
PermitRootLogin no
# Use only SSH Protocol 2
Protocol 2
# Disable empty passwords
PermitEmptyPasswords no
# Allow only specific users (replace with your username)
AllowUsers your_username
# Change default SSH port (optional but recommended)
Port 2222
# Limit authentication attempts
MaxAuthTries 3
Restart SSH to apply changes:
Warning: Before closing your current session, open a new terminal and test SSH login with your new settings to avoid lockout.
Enable Two-Factor Authentication (2FA)
For enhanced ubuntu server security 2026, add 2FA using Google Authenticator:
2
3
4
5
6
sudo <a class="wpil_keyword_link" href="https://www.howto-do.it/what-is-apt-advanced-package-tool/" title="apt" data-wpil-keyword-link="linked" data-wpil-monitor-id="2240">apt</a> update
sudo apt install libpam-google-authenticator -y
# Configure 2FA for your user
google-authenticator
Follow the prompts and scan the QR code with your authenticator app. Then edit PAM configuration:
Add at the top:
Update SSH configuration:
Add or modify:
Restart SSH:
Step 2: Configure UFW Firewall
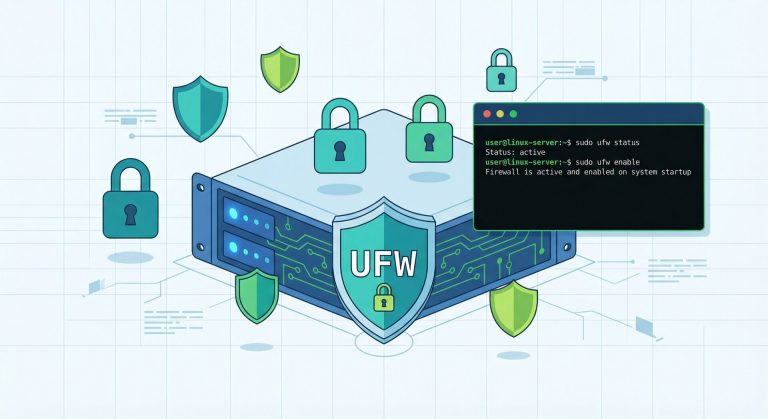
UFW (Uncomplicated Firewall) is Ubuntu’s firewall interface. Proper firewall configuration is essential for ubuntu server security 2026:
Basic UFW Setup
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
sudo ufw status
# Set default policies (deny all incoming, allow all outgoing)
sudo ufw default deny incoming
sudo ufw default allow outgoing
# Allow SSH (use your custom port if you changed it)
sudo ufw allow 2222/tcp
# Or if using default port 22:
# sudo ufw allow 22/tcp
# Allow HTTP and HTTPS if running a web server
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
# Enable UFW
sudo ufw enable
# Verify rules
sudo ufw status verbose
Advanced Firewall Rules for Ubuntu Server Security 2026
Implement rate limiting to protect against brute-force attacks:
2
3
4
5
6
7
8
sudo ufw limit 2222/tcp
# Allow specific IP ranges (e.g., your office network)
sudo ufw allow from 192.168.1.0/24 to any port 2222
# Deny traffic from specific IPs
sudo ufw deny from 203.0.113.0/24
Check logs to monitor blocked connections:
Step 3: Keep Your Ubuntu Server Updated
Regular updates are non-negotiable for ubuntu server security 2026. Unpatched vulnerabilities are the #1 cause of server compromises:
2
3
4
5
6
sudo apt update && sudo apt upgrade -y
# Enable automatic security updates
sudo apt install unattended-upgrades -y
sudo dpkg-reconfigure --priority=low unattended-upgrades
Configure automatic updates to install security patches:
Ensure these lines are uncommented:
2
Unattended-Upgrade::Automatic-Reboot "false";
Monitor security notices at Ubuntu Security Notices.
Step 4: Implement File Permissions and User Management
Proper file permissions prevent unauthorized access. Here’s how to apply them for ubuntu server security 2026:
Set Correct Permissions on Sensitive Files
2
3
4
5
6
7
8
9
10
chmod 700 ~/.ssh
chmod 600 ~/.ssh/authorized_keys
chmod 600 ~/.ssh/id_ed25519
chmod 644 ~/.ssh/id_ed25519.pub
# System configuration files
sudo chmod 600 /etc/ssh/sshd_config
sudo chmod 644 /etc/passwd
sudo chmod 640 /etc/shadow
Create Sudo Users Securely
Never use root directly. Create admin users with sudo privileges:
2
3
4
5
6
7
8
9
sudo adduser newadmin
# Add to sudo group
sudo usermod -aG sudo newadmin
# Verify sudo access
su - newadmin
sudo whoami # Should output: root
Step 5: Monitor Logs and Detect Intrusions
Proactive monitoring is crucial for ubuntu server security 2026. Install fail2ban to automatically block malicious IPs:
2
3
4
5
6
sudo apt install fail2ban -y
# Create local configuration
sudo cp /etc/fail2ban/jail.conf /etc/fail2ban/jail.local
sudo nano /etc/fail2ban/jail.local
Configure SSH protection (find the [sshd] section):
2
3
4
5
6
7
enabled = true
port = 2222
logpath = /var/log/auth.log
maxretry = 3
bantime = 3600
findtime = 600
Restart fail2ban:
2
sudo fail2ban-client status sshd
Review Authentication Logs Regularly
2
3
4
5
6
7
8
sudo grep "Failed password" /var/log/auth.log
# View successful SSH logins
sudo grep "Accepted publickey" /var/log/auth.log
# Monitor real-time authentication events
sudo journalctl -u ssh -f
Step 6: Disable Unnecessary Services
Reduce attack surface by disabling unused services—a key tenet of ubuntu server security 2026:
2
3
4
5
6
7
8
9
10
sudo systemctl list-units --type=service --state=running
# Disable unnecessary services (examples)
sudo systemctl <a class="wpil_keyword_link" href="https://www.howto-do.it/raspberry-pi-disable-bluetooth/" title="disable bluetooth" data-wpil-keyword-link="linked" data-wpil-monitor-id="2239">disable bluetooth</a>.service
sudo systemctl disable cups.service # Printing service
sudo systemctl disable avahi-daemon.service # Network discovery
# Stop them immediately
sudo systemctl stop bluetooth.service cups.service avahi-daemon.service
Step 7: Implement Backup and Recovery
Security isn’t just prevention—it’s also recovery. Implement regular backups:
2
3
4
5
6
7
8
9
10
11
sudo apt install rsync -y
# Create backup directory
sudo mkdir -p /backup
# Example: Backup critical directories
sudo rsync -avz /etc /var/www /home /backup/
# Automate with <a class="wpil_keyword_link" href="https://www.howto-do.it/what-is-cron/" title="cron" data-wpil-keyword-link="linked" data-wpil-monitor-id="2241">cron</a> (daily at 2 AM)
sudo crontab -e
Add this line:
Pro tip: Store backups off-site or in cloud storage. On-server backups won’t help if the entire server is compromised.
Ubuntu Server Security 2026 Checklist
Use this checklist to verify your server meets ubuntu server security 2026 standards:
- ✅ SSH key authentication enabled
- ✅ Password authentication disabled
- ✅ Root login via SSH disabled
- ✅ UFW firewall enabled with minimal open ports
- ✅ Automatic security updates configured
- ✅ Fail2ban installed and monitoring SSH
- ✅ File permissions set correctly
- ✅ Unnecessary services disabled
- ✅ Regular backups automated
- ✅ Logs monitored regularly
Common Ubuntu Server Security 2026 Mistakes to Avoid
Even experienced admins make these errors. Avoid them to maintain robust ubuntu server security 2026:
- Leaving default SSH port 22 open: Change to a non-standard port to reduce automated attacks
- Not testing SSH changes before closing sessions: Always keep a second terminal open when modifying SSH config
- Ignoring security updates: Patches exist because vulnerabilities are actively exploited
- Using weak sudo passwords: A secure SSH key is useless if your sudo password is “password123”
- No firewall rules: Assuming cloud provider firewalls are enough (they’re not—layer your defenses)
- Forgetting log rotation: Logs can fill your disk; ensure logrotate is configured
Advanced Security: AppArmor and SELinux
For maximum ubuntu server security 2026, consider mandatory access control (MAC) systems:
AppArmor (Default on Ubuntu)
2
3
4
5
6
7
8
sudo aa-status
# Enable AppArmor profile for a service
sudo aa-enforce /etc/apparmor.d/usr.sbin.sshd
# View AppArmor logs
sudo journalctl | grep apparmor
AppArmor confines applications to specific permissions, limiting damage if they’re compromised.
Next Steps After Securing Your Ubuntu Server 2026
You’ve implemented core ubuntu server security 2026 practices. Here’s what to do next:
- Schedule quarterly security audits: Revisit configurations every 3 months
- Implement intrusion detection (IDS): Consider tools like AIDE or Wazuh
- Set up centralized logging: Forward logs to a SIEM like Graylog or ELK stack
- Document your configuration: Maintain a security runbook for your team
- Test your backups: Regularly restore from backup to ensure they work
For ongoing learning, bookmark Ubuntu Security Documentation and subscribe to security mailing lists.
Next Steps in Server Hardening: Continue fortifying your stack with our full-scale Ubuntu defense-in-depth security manual, and protect your web applications by configuring an Nginx reverse proxy with SSL certificates.
Conclusion: Ubuntu Server Security 2026 Is an Ongoing Process
Securing your ubuntu server security 2026 deployment isn’t a one-time task—it’s continuous. By following this guide, you’ve established:
- Hardened SSH access with key authentication and 2FA
- Firewall protection via UFW with rate limiting
- Automated security patching
- Log monitoring with fail2ban
- Regular backups for disaster recovery
The threat landscape evolves constantly. Stay informed, keep systems patched, and review logs regularly. Your Ubuntu server is now significantly more secure against 2026’s cyber threats.
Pro tip: Save this checklist and revisit it whenever you deploy a new server. Consistency across your infrastructure is key to maintaining strong ubuntu server security 2026.
For more Linux security tutorials, check out our guides on Debian networking with systemd and Linux firewall best practices.
- About the Author
- Latest Posts

Mark is a senior content editor at Text-Center.com and has more than 20 years of experience with linux and windows operating systems. He also writes for Biteno.com