How to Secure Linux Server SSH Access with Key-Based Authentication 2026

Understanding SSH Security on Linux Servers
When managing a Linux server SSH security setup, one of the most critical steps you can take is implementing key-based authentication instead of relying on passwords. SSH (Secure Shell) is the backbone of remote server administration, but default password authentication leaves your system vulnerable to brute-force attacks and unauthorized access.
In this comprehensive guide, we’ll walk you through how to secure your Linux server SSH access with key-based authentication in 2026. Whether you’re running Ubuntu, Debian, CentOS, or any other distribution, these proven security practices will significantly harden your server against potential threats. If you manage Debian hosts specifically, reference our full Debian Linux server administration handbook for complete system upkeep.
Why Password Authentication is a Security Risk
Traditional password-based SSH authentication has several inherent weaknesses that make it unsuitable for production environments:
- Vulnerable to brute-force attacks using automated tools
- Passwords can be intercepted if weak encryption is used
- Human tendency to reuse passwords across multiple systems
- No audit trail of which key was used for authentication
- Difficulty in revoking access when team members leave
Key-based authentication eliminates these risks by using cryptographic key pairs that are virtually impossible to crack through brute-force methods.
How SSH Key-Based Authentication Works
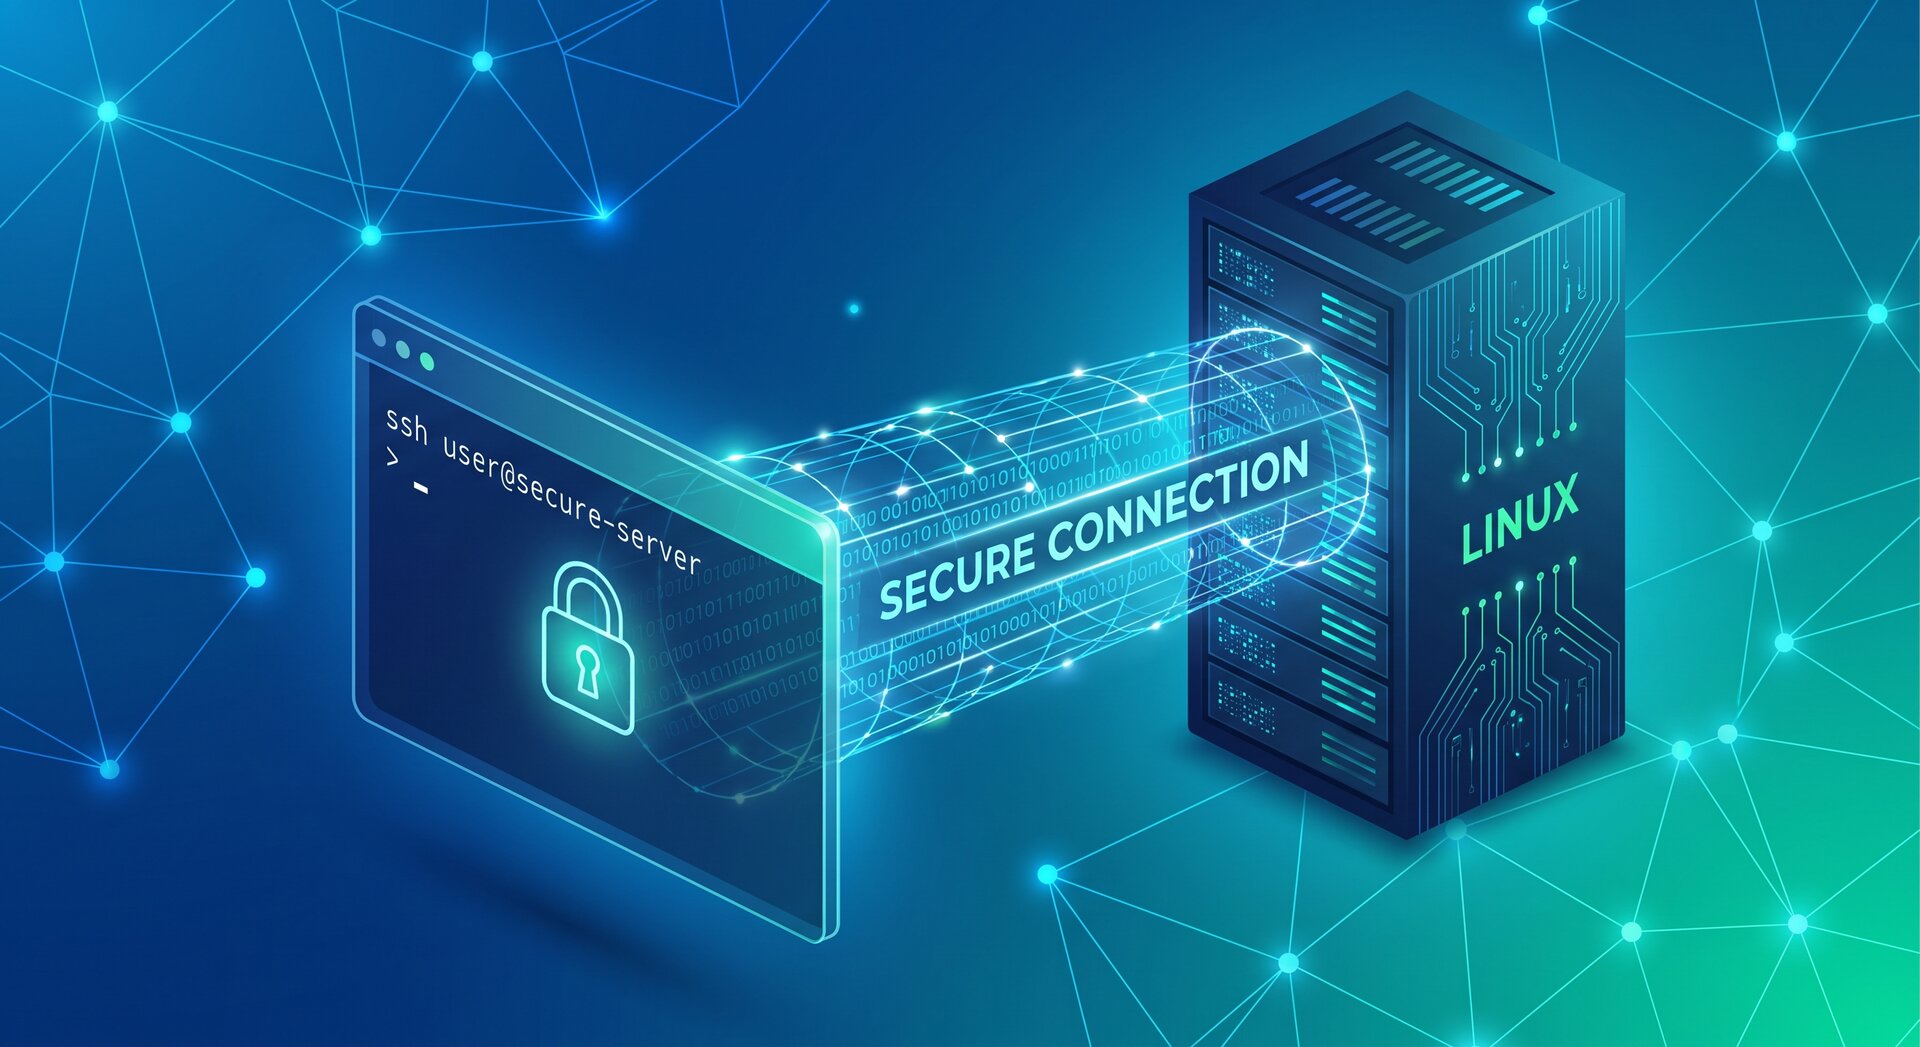
SSH key authentication uses asymmetric cryptography with two components:
- Private Key: Stored securely on your local machine, never shared
- Public Key: Uploaded to the server in the
1~/.ssh/authorized_keys
file
When you connect to a server, the SSH client uses your private key to prove identity without transmitting it over the network. The server verifies this using the corresponding public key, creating a secure authentication mechanism that doesn’t rely on passwords.
Step 1: Generate SSH Key Pair on Your Local Machine
First, open a terminal on your local computer (not the server) and generate a new SSH key pair using the modern Ed25519 algorithm, which provides better security than older RSA keys:
1 | ssh-keygen -t ed25519 -C "[email protected]" |
If your system doesn’t support Ed25519, you can use RSA with a 4096-bit key:
1 | ssh-keygen -t rsa -b 4096 -C "[email protected]" |
During the key generation process, you’ll be prompted to:
- Choose a file location (default:
1~/.ssh/id_ed25519
)
- Enter a passphrase for additional security (recommended)
The passphrase adds an extra layer of protection—even if someone steals your private key file, they cannot use it without the passphrase.
Step 2: Copy Your Public Key to the Linux Server
The easiest way to install your public key on the remote server is using the
1 | ssh-copy-id |
utility:
1 | ssh-copy-id username@server_ip_address |
Replace
1 | username |
with your actual Linux server username and
1 | server_ip_address |
with your server’s IP or hostname. This command will:
- Prompt for your current password (one last time)
- Copy your public key to the server’s
1~/.ssh/authorized_keys
file
- Set correct permissions automatically
If
1 | ssh-copy-id |
is not available, you can manually copy the key:
1 | cat ~/.ssh/id_ed25519.pub | ssh username@server_ip_address "mkdir -p ~/.ssh && cat >> ~/.ssh/authorized_keys" |
Step 3: Test SSH Key Authentication
Before disabling password authentication, verify that key-based login works correctly:
1 | ssh username@server_ip_address |
You should be logged in without entering a password (or only your key passphrase if you set one). If this doesn’t work, check:
- File permissions:
1~/.ssh
should be 700,
1authorized_keysshould be 600
- SSH server logs:
1sudo tail -f /var/log/auth.log
(Ubuntu/Debian) or
1/var/log/secure(CentOS/RHEL)
- SELinux context if applicable
Step 4: Disable Password Authentication
Once you’ve confirmed that Linux server SSH security with key-based authentication works properly, it’s time to disable password login entirely. Connect to your server and edit the SSH daemon configuration:
1 | sudo nano /etc/ssh/sshd_config |
Find and modify these directives (or add them if they don’t exist):
1 2 3 4 | PasswordAuthentication no PubkeyAuthentication yes ChallengeResponseAuthentication no UsePAM no |
Save the file and restart the SSH service:
1 | sudo systemctl restart sshd |
On older systems, you might need to use:
1 | sudo service ssh restart |
Important: Before closing your current session, open a new terminal window and test the connection. This ensures you don’t lock yourself out if something went wrong.
Step 5: Additional SSH Hardening Measures
Beyond key-based authentication, implement these additional security layers for comprehensive Linux server SSH security:
Change the Default SSH Port
While not foolproof, changing from port 22 to a non-standard port reduces automated attack attempts:
1 | Port 2222 |
Add this line to
1 | /etc/ssh/sshd_config |
, then restart SSH. Remember to update your firewall rules accordingly.
Disable Root Login
Prevent direct root access via SSH:
1 | PermitRootLogin no |
Use a regular user account with sudo privileges instead.
Limit User Access
Restrict SSH access to specific users:
1 | AllowUsers user1 user2 user3 |
Or allow specific groups:
1 | AllowGroups sshusers |
Enable Two-Factor Authentication
For even stronger security, combine SSH keys with Google Authenticator or similar OTP solutions using PAM modules.
Managing Multiple SSH Keys
If you manage multiple servers or have different keys for different purposes, use an SSH config file to organize them:
1 | nano ~/.ssh/config |
Add entries like:
1 2 3 4 5 | Host myserver HostName server_ip_address User username IdentityFile ~/.ssh/id_ed25519_myserver Port 2222 |
Now you can connect simply with
1 | ssh myserver |
instead of remembering all the details.
Monitoring and Auditing SSH Access
Implement regular monitoring to detect unauthorized access attempts:
- Review
1/var/log/auth.log
regularly for failed login attempts
- Use tools like
1fail2ban
to automatically block IPs after repeated failures
- Set up log aggregation with tools like ELK stack or Graylog
- Enable SSH login notifications via email or messaging systems
Backup and Recovery Considerations
After securing your Linux server SSH security setup, ensure you have a recovery plan:
- Keep encrypted backups of your private keys in a secure location
- Document the recovery process for team members
- Maintain console access through your hosting provider’s control panel
- Create an emergency admin account with a strong password (disabled for SSH but available via console)
Common Troubleshooting Issues
Permission Denied (publickey)
Check file permissions:
1 2 | chmod 700 ~/.ssh chmod 600 ~/.ssh/authorized_keys |
Connection Refused
Verify the SSH service is running:
1 | sudo systemctl status sshd |
Too Many Authentication Failures
If you have multiple keys, SSH might try them all and get blocked. Use the
1 | -i |
flag to specify the correct key:
1 | ssh -i ~/.ssh/specific_key username@server |
Best Practices for Long-Term Security
Maintaining robust Linux server SSH security requires ongoing attention:
- Rotate SSH keys annually or when team members leave
- Keep your SSH client and server software updated
- Use strong key algorithms (Ed25519 or RSA 4096-bit minimum)
- Implement network-level security with firewalls and VPNs
- Document your security procedures for team members
- Regularly audit which keys have access to which servers
Conclusion
Implementing proper Linux server SSH security with key-based authentication is one of the most effective ways to protect your infrastructure from unauthorized access. By following the steps outlined in this guide, you’ve significantly hardened your server against common attack vectors.
Remember that security is an ongoing process, not a one-time setup. Regularly review your configuration, monitor access logs, and stay informed about emerging threats and best practices. The time invested in securing SSH access today will save you from potential breaches and data loss tomorrow.
For production environments, consider implementing additional layers such as jump hosts, VPN access requirements, and intrusion detection systems, as detailed in our guide to hardening your Ubuntu production server. Combined with the key-based authentication setup you’ve just completed, these measures create a comprehensive defense strategy for your Linux infrastructure.
- About the Author
- Latest Posts

Mark is a senior content editor at Text-Center.com and has more than 20 years of experience with linux and windows operating systems. He also writes for Biteno.com